Amadeus Data Breach 2026: Best Warning for Indian Air Travelers on 7 Airlines
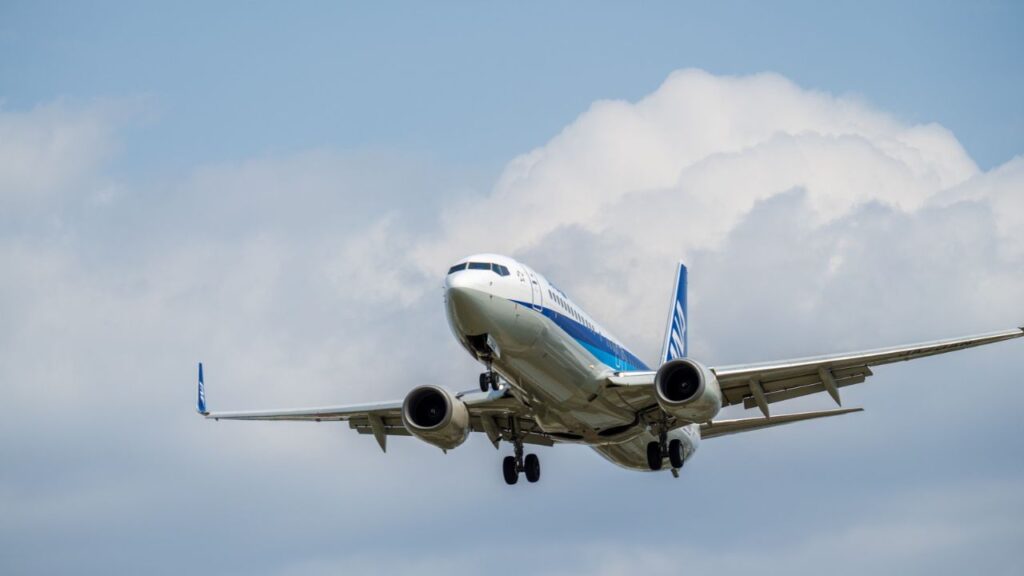
The Amadeus data breach 2026 affected over 180,000 passengers across Japan Airlines, ANA, Cathay Pacific, Korean Air and other carriers using the Altéa reservation system.
Quick Answer: A three-year data breach at aviation technology giant Amadeus has exposed passenger data from at least 5–7 major airlines including Japan Airlines, ANA, Cathay Pacific, Korean Air, and Condor — affecting nearly 200,000 travelers worldwide.
The Amadeus data breach 2026 is one of the most serious aviation cybersecurity incidents in recent years. Amadeus, a technology provider whose Altéa platform powers flight bookings, check-in, and reservation management for more than 130 international airlines, suffered unauthorized access to its systems for over three years — from August 2023 to September 2026. The Amadeus data breach 2026 has now been confirmed by multiple airlines, with passenger names, passport numbers, booking references, and frequent flyer details among the data exposed.
Amadeus Data Breach 2026: Which Airlines Were Affected?
The Amadeus data breach 2026 has been confirmed by five airlines so far, with reports suggesting the actual number could be higher given that the Altéa platform serves over 130 carriers globally. The breach went undetected for more than three years, meaning passengers who flew on any of these airlines between August 2023 and September 2026 may have had their data accessed.
The five confirmed airlines are Japan Airlines (JAL), All Nippon Airways (ANA), Cathay Pacific, Korean Air, and German carrier Condor. Asiana Airlines has also confirmed it was affected, though no passenger count has been disclosed. For Indian travelers, this is particularly relevant — Cathay Pacific, Japan Airlines, ANA, and Korean Air are among the most popular carriers used by Indians flying to Japan, Hong Kong, South Korea, and onward to North America.
| Airline | Passengers Affected | Data Exposed |
|---|---|---|
| Japan Airlines (JAL) | ~90,000 | Names, PNR codes, routes, travel class; passports for ~2,000 |
| ANA All Nippon Airways | ~37,800 | Names, reservation numbers, travel dates; passports for ~1,700 |
| Cathay Pacific | ~53,000 bookings | Names, booking refs, flight details; contacts & travel docs for subset |
| Korean Air | Not disclosed | Confirmed affected |
| Condor | Not disclosed | Confirmed affected |
| Asiana Airlines | Not disclosed | Confirmed affected |
What Passenger Data Was Exposed in the Amadeus Data Breach 2026?
The Amadeus data breach 2026 exposed different categories of data depending on which airline you flew and whether your booking was part of the more deeply compromised subset. For the majority of affected passengers, the data exposed includes booking reference codes (PNR), passenger names, flight dates, routes, and travel class.
For a smaller but significant group — approximately 3,700 travelers across JAL and ANA alone — the breach exposed passport numbers, nationalities, email addresses, phone numbers, frequent flyer numbers, seat numbers, and ticket numbers. Cathay Pacific confirmed a subset of its 53,000 affected bookings also had travel document numbers and contact details accessed.
The critically important point for affected travelers: no credit card numbers, passwords, or payment information has been reported as exposed by any airline. However, the combination of passport numbers, booking references, and contact details is more than enough for sophisticated phishing attacks and identity fraud.
| Data Category | Exposed? |
|---|---|
| Passenger name | ✅ Yes — all affected passengers |
| Booking reference (PNR) | ✅ Yes — all affected passengers |
| Flight dates and routes | ✅ Yes — all affected passengers |
| Email address and phone number | ✅ Yes — subset of passengers |
| Passport number and nationality | ✅ Yes — ~3,700+ passengers confirmed |
| Frequent flyer number | ✅ Yes — subset of passengers |
| Credit card or payment details | ❌ No — not reported as exposed |
| Passwords | ❌ No — not reported as exposed |
Timeline of the Amadeus Data Breach 2026
The Amadeus data breach 2026 is alarming not just for what was exposed but for how long it went undetected. Unauthorized access to the Amadeus Altéa passenger service system began on 10 August 2023 and continued until 23 September 2026 — a span of over three years.
Amadeus issued an initial statement on 1 October 2026, acknowledging a vulnerability in its travel booking display environment. The company said at that point that ransomware actors had not exploited the flaw and no payment data was exposed. Amadeus notified Japan Airlines on 23 October 2026. Cathay Pacific was informed of the breach on 28 October 2026 and disclosed it publicly the following day.
The method of entry appears to involve social engineering — attackers reportedly tricked IT helpdesk personnel into issuing legitimate login credentials, giving them prolonged undetected access to the reservation system.
What Indian Travelers Should Do Right Now
For Indian passengers who have flown on Cathay Pacific, Japan Airlines, ANA, Korean Air, Asiana, or Condor at any point between August 2023 and September 2026, the following steps are strongly recommended.
1 — Watch for phishing emails very carefully. Because attackers have your name, booking reference, flight details, and possibly your email and phone, any phishing email pretending to be from your airline will look highly convincing. It may reference your actual flight number, travel dates, and seat number to appear legitimate.
2 — Never click links in unexpected airline emails. Go directly to the airline’s official website by typing the URL in your browser. Do not click links in emails claiming to be about refunds, rebooking, loyalty points, or “security alerts.”
3 — Monitor your passport for misuse. If your passport number was part of the exposed data, keep an eye on any notifications from immigration or border control authorities. Report suspicious activity to your airline and local authorities.
4 — Check your frequent flyer account. Log in directly to your airline loyalty account and verify that no unauthorised redemptions or changes have been made. Enable two-factor authentication if available.
5 — Contact your airline directly. JAL, ANA, and Cathay Pacific have all said they will notify affected passengers. If you haven’t heard from your airline and believe you may be affected, contact their customer service through official channels.
6 — Be extra cautious with travel-related calls. Scammers may use your booking details to call you posing as airline staff or travel agents. Never share additional personal or financial information over a call you did not initiate.
FAQs — Amadeus Data Breach 2026
Q1: How do I know if my data was exposed in the Amadeus data breach 2026?
The affected airlines — Japan Airlines, ANA, Cathay Pacific, Korean Air, Condor, and Asiana — are in the process of notifying affected passengers directly. If you flew on any of these airlines between August 2023 and September 2026 and booked through a system powered by Amadeus Altéa, your data may have been accessed. Watch for official notifications from your airline via your registered email address.
Q2: Was my credit card or payment data stolen in the Amadeus data breach 2026?
No airline has reported that credit card numbers, payment details, or passwords were exposed in the Amadeus data breach 2026. The exposed data primarily includes passenger names, booking references, flight details, and for a smaller subset, passport numbers, email addresses, phone numbers, and frequent flyer information. However, this information is still sensitive enough to enable phishing attacks.
Q3: Should Indian travelers avoid flying these airlines after the Amadeus data breach 2026?
The Amadeus data breach 2026 affected historical passenger data — it did not compromise current flight operations or safety systems. All affected airlines have confirmed that flight operations were not disrupted. Indian travelers do not need to avoid these airlines, but should remain alert to phishing attempts, monitor their passport and loyalty accounts, and follow all official communications from their respective carriers closely.
Final Word
The Amadeus data breach 2026 is a serious wake-up call for the global aviation industry and for Indian travelers who regularly use international carriers. With over 180,000 passengers potentially affected across at least six airlines — and the breach running silently for over three years — the scale of exposure is significant. Indian passengers who have flown Cathay Pacific, Japan Airlines, ANA, or Korean Air in the last three years should stay vigilant, check official airline communications, and take immediate steps to protect their personal data. Stay alert, avoid clicking suspicious links, and always verify communications through official airline websites.
Also Read:
- UAE Travel Advisory July 2026: Important Warning for Indian Travelers
- Singapore Haze 2026: Key Travel Warning for Indians Visiting Singapore
- Air India Singapore Airlines 2026: New Partnership Updates for Indians
Official Sources:
 Amadeus Data Breach 2026: Best Warning for Indian Air Travelers on 7 Airlines
Ireland Visa Waiver Indians 2026: Best Complete Guide Until December
Thailand Tourism Strategy 2027: 5 Asian Markets Targeted, What It Means for Indians
Singapore Haze 2026: PSI 192 Peak, Health Warnings, and What Indian Tourists Must Know
Amadeus Data Breach 2026: Best Warning for Indian Air Travelers on 7 Airlines
Ireland Visa Waiver Indians 2026: Best Complete Guide Until December
Thailand Tourism Strategy 2027: 5 Asian Markets Targeted, What It Means for Indians
Singapore Haze 2026: PSI 192 Peak, Health Warnings, and What Indian Tourists Must Know

Aaseem Bhardwaj is a journalist, seasoned traveler and IT professional based in India. With firsthand travel experience across Southeast Asia, East Asia, Middle East and Europe, Aaseem founded Travel Man Today to provide reliable visa updates and travel news for Indian passport holders. He has personally traveled to Thailand, Vietnam, Malaysia, Japan, Singapore, Hong Kong, South Korea, UAE and Europe. Follow his travel vlogs on YouTube at @travelmantoday


Templates for Indians